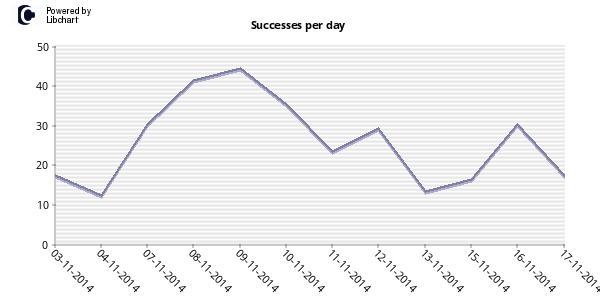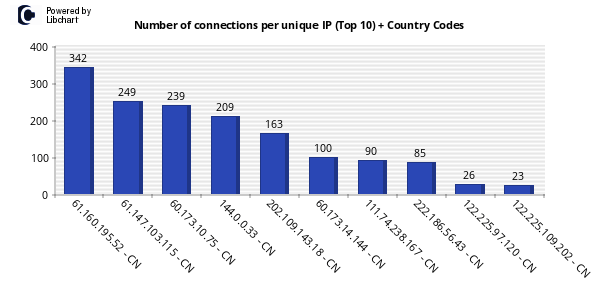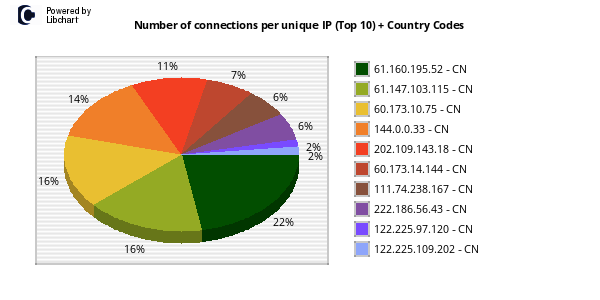
I recently set up a honeypot tool called Kippo. Kippo runs a virtual SSH environment and records every SSH brute-force attempt against the server. We started the capture on 3 November and saw about 4,000 brute-force attempts against the server; what stands out is that almost all of the login attempts came from hosts based in China.
Our research showed that almost all the attacking machines run the Windows IIS Webserver, we are not sure whether those machines are zombies (compromised hosts being used to attack others) or servers stood up deliberately to sweep wide ranges. So far we have collected about 2,500 distinct username/password combinations.
Top credentials#
The Top 10 List of combinations is below:
| Username | Password |
|---|---|
| root | admin |
| admin | passw0rd |
| admin | password |
| admin | P@ssw0rd |
| admin | abc123 |
| admin | admin |
| admin | admin |
| admin | 1qaz@WSX |
| admin | Admin123!@# |
Attack trends#
I collected some charts of the attack trends below.